When an AI assistant only summarizes a document, the main risk is usually the quality and safety of the output. When an AI agent can read business data, call tools, update records, route work, draft messages, or ask for approval to take action, the risk profile changes.
That is the practical point running through recent AI security guidance from OWASP, Microsoft, and Unit 42. The warning is not that every business should avoid agents. It is that tool access, memory, coordination, and approval authority need to be designed before an agent becomes part of daily operations.
For business owners, COOs, IT owners, and operations leaders, ai agent security is less abstract than it sounds. It starts with a simple question: what can this agent see, remember, decide, request, and do?
Why tool-using agents need a different review
Traditional automation often follows deterministic rules: if a form arrives, create a task; if a field is missing, route an exception; if a report is due, send a reminder. AI-assisted workflows add interpretation. Agentic workflows go further by combining interpretation with tool use.
That creates new review points:
- the data the agent can read;
- the tools it can call;
- whether those tools are read-only or read-write;
- what the agent can store in memory or context;
- which actions require a person;
- what gets logged when the agent makes or requests a decision;
- what happens when the agent is uncertain, manipulated, or wrong.
OWASP’s AI Agent Security Cheat Sheet treats these as design concerns, not afterthoughts. It highlights least privilege, prompt-injection defense, memory and context controls, human approval, monitoring, data protection, multi-agent security, and adversarial validation as practical areas to review.
Microsoft’s June 30, 2026 security post makes the same issue concrete: once agents move from reading to acting, tool descriptions, tool metadata, and permission boundaries can become part of the security surface. A tool may look approved by name, while its instructions or behavior change in ways the agent treats as trustworthy.
That matters because many business workflows are built from ordinary tools: inboxes, documents, spreadsheets, CRMs, finance records, task systems, approval queues, support tickets, and public web sources. If an agent can connect those pieces, ai agent governance must cover the whole workflow, not only the model.
The hidden input problem: indirect prompt injection
The Palo Alto Networks Unit 42 analysis, accessed 2026-07-27, is especially relevant for businesses that want agents to browse, summarize, classify, monitor, or review online content.
The defensive idea is straightforward: an attacker does not always need to talk to the agent directly. Malicious or manipulated instructions can be placed inside web pages, metadata, comments, documents, or other content the agent later consumes. If the agent treats that content as instructions instead of untrusted data, it may be pushed away from its intended task.
This is why indirect prompt injection becomes more serious when the same agent also has business privileges. A summarizer might produce a biased or strange summary. A tool-using agent with write access, external messaging rights, financial context, or approval authority can create a more consequential failure.
The business takeaway is not to reproduce attack examples or chase every new tactic. It is to define trust boundaries:
- What content is untrusted by default?
- Can the agent separate instructions from data?
- Are web pages, emails, attachments, retrieved documents, and customer messages treated as inputs to inspect rather than commands to obey?
- Are high-impact actions blocked until an authorized person reviews the underlying evidence?
- Is the reviewer shown the real action and affected records, not just the agent’s friendly explanation?
Approval authority is a workflow design issue
Many teams describe their safety control as “human review.” That is a good starting point, but it is not specific enough.
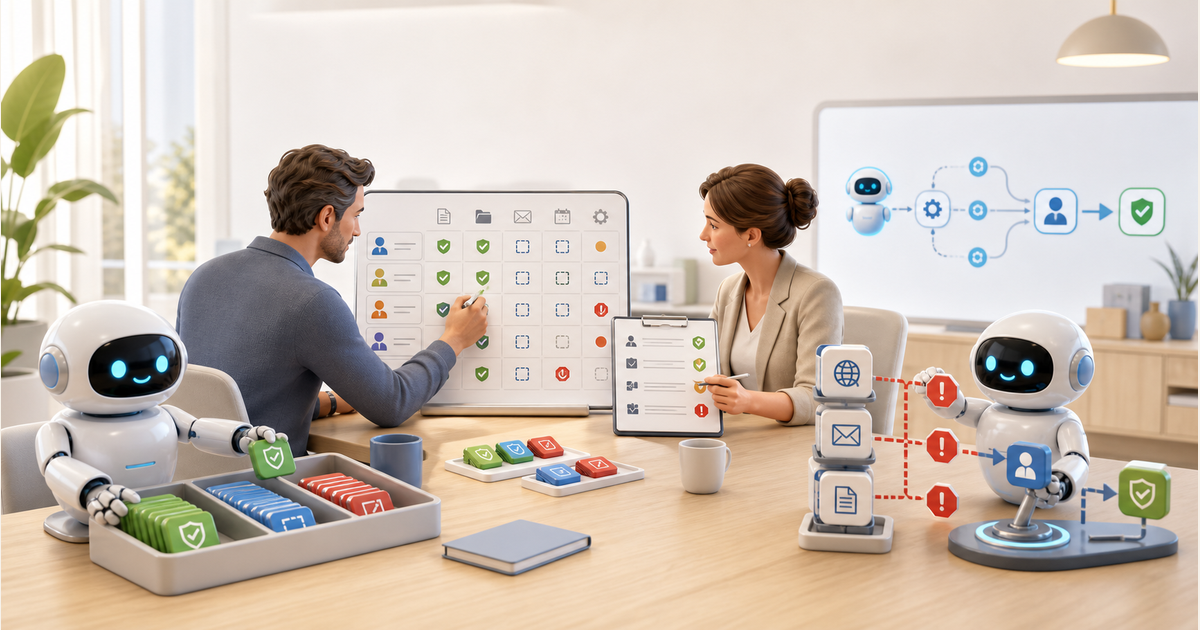
A practical human in the loop ai design should answer several operational questions. Who is the reviewer? What authority do they have? What exactly do they see before approving? Can they reject or edit the proposed action? Is approval required every time, only above a risk threshold, or only when confidence is low? Can the agent split a risky action into smaller steps that look harmless one by one?
Microsoft’s June 4, 2026 taxonomy update calls attention to system-level failure modes that are easy to miss if the review focuses only on model output. Goal hijacking, inter-agent trust escalation, session context contamination, plugin or tool abuse, and human-approval bypass are not solved by a prettier approval button. They require workflow-level threat modeling.
For a business process, that means approvals should be tied to action risk. Reading a public document is not the same as updating a customer record. Drafting a message is not the same as sending it. Preparing a finance exception queue is not the same as approving payment. Summarizing a security alert is not the same as taking containment action.
What to map before expanding agent access
Before giving an automation agent more authority, businesses can review the proposed workflow in plain operational terms.
Start with purpose and ownership. The agent should have a defined job, a process owner, a data owner, and a named person who can pause or change the workflow. If nobody owns the result, the agent should not own the action.
Map the data path. Identify which sources the agent reads, which data is sensitive, what enters the prompt or context, what may be stored, and what should be redacted or excluded. Do the same for logs: useful monitoring should not turn into unnecessary sensitive-data retention.
Inventory tools and permissions. List every tool the agent can call and classify it as read, draft, write, external-send, administrative, financial, destructive, or irreversible. Default to read-only where possible. Separate low-risk tools from high-impact tools.
Review tool metadata and change control. If an agent uses natural-language tool descriptions to decide when and how to call tools, those descriptions deserve review. A change to a production tool description can change agent behavior even when the visible tool name stays familiar.
Define approval gates. Decide which actions require explicit human approval: external messages, administrative changes, access grants, contract commitments, public statements, financial actions, deletions, and other consequential outcomes. The approver should see the affected records, proposed action, reason, source evidence, and rollback or fallback option where applicable.
Plan monitoring and recovery. Logs should capture inputs, decisions, tool calls, approval results, errors, and configuration changes at an appropriate privacy level. Exception queues, retries, circuit breakers, manual fallback, and rollback paths should be part of the design before launch.
Test realistic failure modes. For discovery-stage planning, that may mean reviewing prompt-injection exposure, memory/context handling, approval-bypass paths, tool misuse, and cross-agent handoffs. Formal red-team methodology is a separate specialist-validation area, but basic adversarial thinking belongs in discovery.
How KeepSolid Automations can help explore the question
KeepSolid Automations is a managed service for turning repetitive business work into custom, AI-powered automated systems. For this topic, the relevant offer readiness is discovery-ready: KeepSolid Automations may help a business explore an ai agent security assessment for proposed or existing automation workflows before implementation or expansion.
That discovery can focus on practical workflow questions rather than broad security claims:
- Which business process is the agent supposed to support?
- Which triggers, inputs, systems, rules, owners, approvals, exceptions, and outputs are involved?
- What data and tools would the agent need?
- Which actions can remain deterministic?
- Where should AI only classify, extract, summarize, or draft?
- Where must a person retain approval authority?
- What monitoring, logs, exception queues, and fallback paths are needed?
- Which areas require security, privacy, legal, finance, HR, or domain-specialist validation before any delivery commitment?
This framing keeps the work grounded. It does not treat the agent as a self-service software feature that can be switched on safely by default. It treats the agent as part of a managed business process with permissions, owners, and operating controls.
A leadership checklist before agent authority expands
If your team is already experimenting with agents, ask these questions before giving them broader access:
- What is the smallest useful scope for this agent?
- Can the first version operate with read-only access or draft-only actions?
- Which systems, records, and fields are out of scope?
- Which external inputs could carry malicious or misleading instructions?
- What does the agent remember, and when does that memory expire?
- Which actions need approval every time?
- Who can approve, reject, pause, or roll back the workflow?
- Are approval prompts based on underlying tool calls and source evidence?
- Are tool permissions and descriptions reviewed when they change?
- Can logs show what happened without exposing unnecessary sensitive data?
- What failure would be merely inconvenient, and what failure would be consequential?
- Which parts need specialist validation before moving forward?
These questions are useful even when the answer is “not yet.” In many cases, the safest next step is not to abandon the agent idea. It is to narrow the workflow until the business can see the access, actions, approvals, and risks clearly.
FAQ
Is an AI-agent security assessment the same as a certification?
No. In this context, an ai agent security assessment is a discovery-oriented review of a proposed or existing automation workflow. It can help map risk areas, access needs, approval boundaries, monitoring needs, and validation questions. It is not a certification, compliance guarantee, penetration test, formal red-team package, or security conclusion.
Should every AI agent require human approval?
Not for every low-risk step. A useful design usually separates low-risk read or draft actions from high-impact actions. Human approval should be explicit for external, destructive, administrative, financial, irreversible, public, or otherwise consequential outcomes.
Does prompt injection matter if the agent only reads data?
Yes, but the impact is different. Prompt injection against a reading-only assistant may distort a summary or classification. The concern grows when the same agent can call tools, access sensitive records, write to systems, send messages, or influence approvals.
What should a business do first?
Start with one workflow. Map the agent’s purpose, inputs, tools, data access, memory, approval points, logs, exception handling, and fallback path. Then decide whether the workflow is suitable for discovery, needs a narrower pilot, or requires specialist validation before any implementation commitment.
Before the next agent pilot
AI agents can support useful business workflows, but authority should not arrive by accident. The moment an agent can use tools or request approval for real actions, security becomes part of process design.
KeepSolid Automations can help businesses explore this through discovery: mapping the workflow, identifying permissions and approval boundaries, reviewing data and context handling, and clarifying which risk areas need additional validation before implementation or expansion.